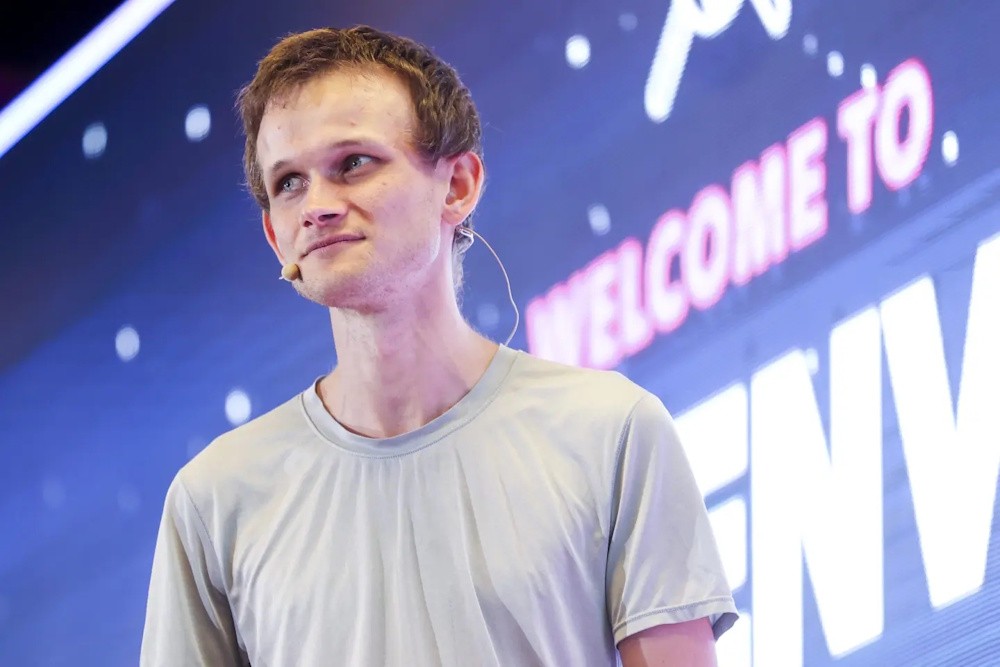
Ethereum co-founder Vitalik Buterin asserts that AI does not signify the demise of cybersecurity. He contends that sophisticated models could enhance the resilience of crypto software against breaches. In a Wednesday post on X, Buterin contended that AI will not provide hackers with an overwhelming advantage, noting that crypto holders-including himself, with approximately 90% of his net worth in crypto-are wagering that security measures can evolve accordingly. “It’s an increasingly common take that AI hacking means cybersecurity is doomed,” Buterin wrote. “I disagree. I think cybersecurity is naturally defense-favoring once people get their shit together.” Buterin contended that AI has the potential to render formal verification-the application of mathematical proofs to confirm the security of software-feasible, even for intricate systems. “If AI can prove Navier-Stokes and FLT, then AI can prove the statement ‘this program is secure’ as a mathematical theorem,” he wrote.
“Even if the program is very complicated.” In other words, Buterin posits that AI, when sufficiently advanced, could not only tackle notoriously challenging mathematical problems but also demonstrate that even intricate software adheres to well-defined security standards. That does not imply, however, that security is straightforward, he stated. The challenging aspect lies in establishing a clear definition of what constitutes “secure” in the initial instance. Blockchain developers are increasingly employing AI agents to analyse code, test for exploits, and verify bugs prior to potential attacks, as researchers identify vulnerabilities within both Ethereum infrastructure and Bitcoin software. Developers throughout the cryptocurrency sector are implementing AI measures in a defensive manner, prompted by a series of incidents that have heightened concerns regarding the potential advantages AI may confer to attackers.
In May, security researcher Taylor Hornby utilised Anthropic’s Claude Opus 4.8 to identify a four-year-old vulnerability in Zcash’s Orchard privacy pool, which had the potential to facilitate unlimited, undetectable counterfeiting of ZEC. However, developers reported no evidence of prior exploitation before they implemented a patch in June. The competition between attackers and defenders intensified in July, as researchers from the Ethereum Foundation reported that AI agents had identified vulnerabilities in essential network infrastructure. That same month, attackers initiated the draining of Coldcard wallets by exploiting a long-standing firmware vulnerability that compromised seed generation, resulting in the theft of approximately $130 million in Bitcoin. Coinkite, the manufacturer of Coldcard, indicated that artificial intelligence probably played a role in detecting the bug.
By August, the threat had permeated the Bitcoin software ecosystem. Boltz has suspended its swap service, citing that suspected attackers were exploiting vulnerabilities more rapidly than its developers could address them. Meanwhile, Core Lightning has verified that several vulnerabilities identified in AI-generated reports were indeed legitimate. In response, the volunteer Bitcoin Red Team employed AI-assisted audits to identify 4,962 potential vulnerabilities across 390 projects. Buterin stated that AI is now capable of verifying entire programs instead of just select components, a strategy that Ethereum intends to adopt in the coming years. “There is no future for blockchains-especially blockchains with scalability and privacy-without doing this,” he said. “We need to make software actually secure. And we have already made a lot of progress.”